Indonesia's National Cyber and Crypto Agency (BSSN) recorded around 5.5 billion cyberattacks detected during 2025. In June 2026 a cybersecurity firm working in Indonesia said ransomware no longer targets only banks but also hospitals and manufacturers, and that attackers have begun using artificial intelligence (AI) to find weaknesses and speed up their attacks (Wandira, 2026).
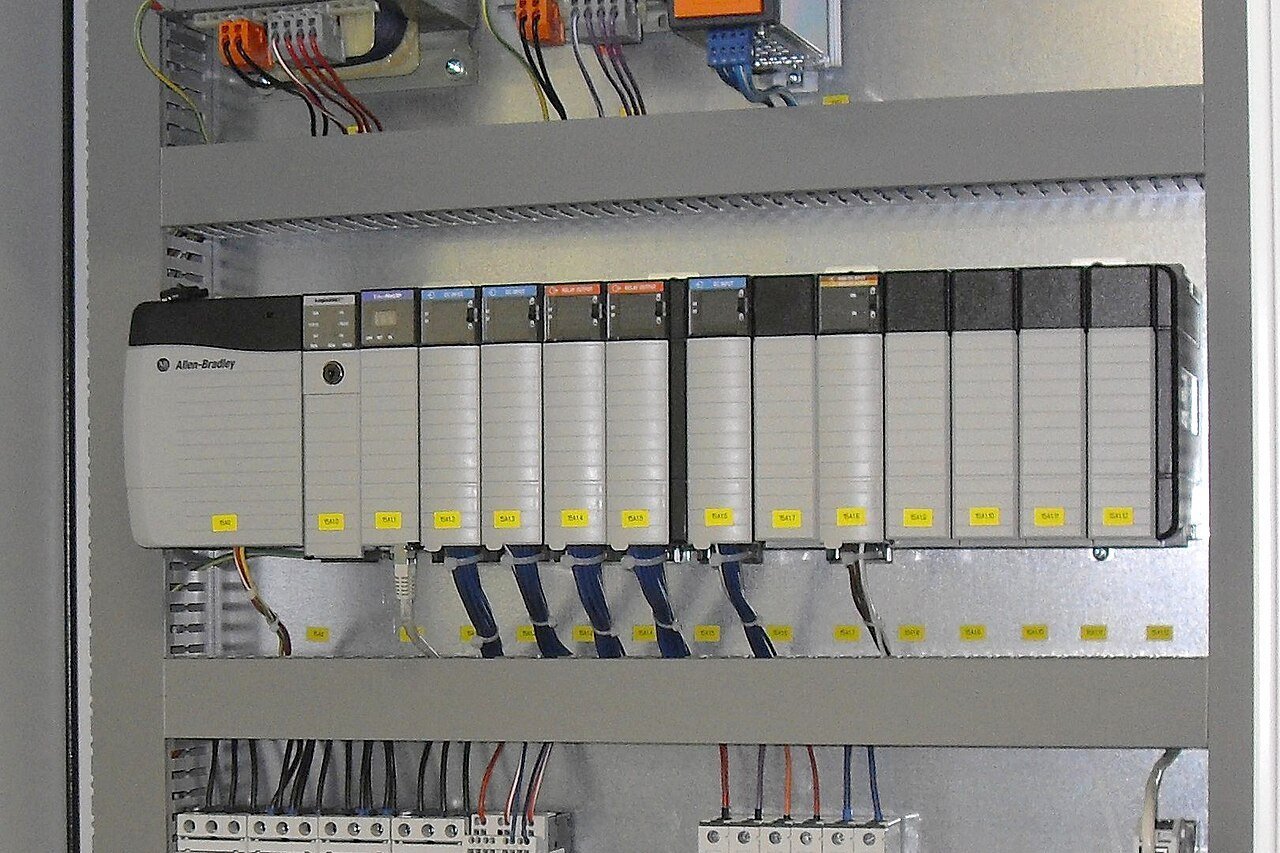
A warning closer to the production floor came on 19 August 2026. The US National Security Agency, Cybersecurity and Infrastructure Security Agency, Federal Bureau of Investigation, Department of Energy and Environmental Protection Agency stated that Siemens S7 programmable logic controllers (PLCs) are being actively targeted, including the S7-1500 series, which covers F-series safety controllers. The actors use internet scanning services to find PLCs that are exposed to the internet or poorly segmented, take advantage of default credentials, and run AI-generated scripts disguised as monitoring tools to read and write PLC memory. The most targeted sectors include critical manufacturing, energy, water and wastewater, chemicals, and food and agriculture, and exploitation could lead to process disruption, safety incidents or equipment damage (National Security Agency [NSA] et al., 2026). This case study looks at one event that shows where such a threat can lead: the Triton attack of 2017.
The Indictment Timeline
Official US government documents on this event do not name the facility. The official source used here is an indictment, which sets out allegations rather than a court verdict. According to the US Department of Justice, between May and September 2017 the defendants hacked the systems of a foreign refinery and installed malware known as Triton on safety systems made by Schneider Electric. The malware was designed to prevent the refinery's safety systems from functioning. The attempt caused the safety systems to initiate two automatic emergency shutdowns (U.S. Department of Justice [DOJ], 2022).
Contributing Factors
A study of 82 cybersecurity-related incidents in the process industry and similar sectors, such as chemicals, petrochemicals, energy production and water and wastewater treatment, mapped the general steps of an attack on automated control systems, the hacking techniques most often used and the countermeasures available. The same study stressed that a cyberattack can trigger major events such as releases of hazardous materials, fires and explosions (Iaiani et al., 2021). The August 2026 advisory adds more practical factors: devices connected directly to the internet, outdated software, default credentials, and remote access by service providers or system integrators that asset owners often do not realise exists (NSA et al., 2026).
Protection Layer Analysis
In process risk studies such as LOPA, the safety instrumented system (SIS) is credited as a protection layer independent of the basic process control system. In our view, Triton shows that this independence is not a built-in property of the hardware but the result of design and management. When the SIS can be reached from the same network as the control system, or from an engineering workstation linked to the office network, one attack path can weaken two layers at once, and the risk reduction claimed in the LOPA becomes too optimistic. The 2016 edition of IEC 61511-1 already requires a security risk assessment for the SIS (International Electrotechnical Commission [IEC], 2016), but that requirement only matters when its results feed into HAZOP, LOPA and management of change.
The early warning sign also deserves attention. In this case, what was visible from outside was an automatic shutdown. A trip with no clear cause is easy to log as an ordinary instrument fault, even though it may be the only early clue. The 2026 advisory also states that AI dramatically reduces the expertise and time needed to build PLC attack tools (NSA et al., 2026). We read this as a sign that the range of actors able to attack plant controllers will keep widening.
Lessons for Plants
- Inventory every PLC and SIS, including which ones can be reached from the internet or from the office network.
- Remove direct internet access to controllers, and route service provider remote access through a controlled, logged and supervised path.
- Replace default credentials and apply security updates as the manufacturer recommends.
- Add cyber scenarios to HAZOP and LOPA, and treat every change to controller logic as a managed change.
- Investigate unexplained trips with instrumentation and IT/OT teams together.
- Rehearse cyber incident response with operations and emergency response teams.
From the process safety side, Nusa Safety can help add cyberattack scenarios to HAZOP & LOPA Studies, review management of change and the integrity of protection layers through a Process Safety Management Review, and design digital reporting and follow-up flows through HSE Digitalization, working alongside the company's IT/OT team. Nusa Safety issues internal training certificates only and is not a PJK3. To discuss the needs of a specific facility, please contact the Nusa Safety team.
This article is general information and not legal or professional advice for any specific case.
References
- Iaiani, M., Tugnoli, A., Bonvicini, S., & Cozzani, V. (2021). Analysis of cybersecurity-related incidents in the process industry. Reliability Engineering & System Safety, 209, 107485. https://doi.org/10.1016/j.ress.2021.107485
- International Electrotechnical Commission. (2016). Functional safety - Safety instrumented systems for the process industry sector - Part 1 - Framework, definitions, system, hardware and application programming requirements (IEC 61511-1:2016). https://webstore.iec.ch/en/publication/24241
- National Security Agency, Cybersecurity and Infrastructure Security Agency, Federal Bureau of Investigation, Department of Energy, & Environmental Protection Agency. (2026). Defending against an active threat to Siemens S7 Series PLCs (Joint Cybersecurity Advisory, TLP:CLEAR). https://www.ic3.gov/CSA/2026/260819.pdf
- U.S. Department of Justice. (2022, March 24). Four Russian government employees charged in two historical hacking campaigns targeting critical infrastructure worldwide. https://www.justice.gov/opa/pr/four-russian-government-employees-charged-two-historical-hacking-campaigns-targeting-critical
- Wandira, L. (2026, June 19). BSSN catat 5,5 miliar serangan siber, industri RI hadapi ancaman AI hingga ransomware [BSSN records 5.5 billion cyberattacks as Indonesian industry faces threats from AI to ransomware]. Kontan. https://nasional.kontan.co.id/news/bssn-catat-55-miliar-serangan-siber-industri-ri-hadapi-ancaman-ai-hingga-ransomware